Next.js Is Shipping an Out-of-Band Security Patch on October 14: Two Changes to the Runbook We Wrote in August
Next.js will publish an out-of-band security update on October 14 with three vulnerabilities in upstream dependencies — two Critical and one High — two of them postponed from the September release. What to prepare in the next 48 hours, and how to decide on Wednesday morning without either panicking or waiting a week.
Next.js Is Shipping an Out-of-Band Security Patch on October 14: Two Changes to the Runbook We Wrote in August
Next.js will publish an out-of-band security update this Wednesday, October 14: three vulnerabilities in upstream dependencies — two Critical and one High — with two of them postponed from the scheduled September release. The full advisories land the same day, so there is no patched version number to target today. The only decision you actually make right now is how you arrive at Wednesday, and that is where a runbook built on «patches are calendar events» comes up short. We wrote that runbook in August. This week it needs two changes.
What was announced on October 8
On October 8, Josh Story, Karim Rahal and Sebastian Silbermann published a Next.js blog post in a structure by now familiar to us: date, severity, vulnerability count, and a promise of a full advisory on release day. The sentence that changes the script is this one: «Two of these fixes were postponed from the September security release due to upstream coordination».
In other words, two of the three holes have been known since September. Detection did not fail; coordination with an external project Next.js depends on did. And when that happens, the date sitting in your calendar stops being trustworthy.
The third vulnerability is the arithmetic that does not quite close: the notice describes two Critical and one High, while September postponed one Critical and one High. Either a new Critical appeared since then or the classification shifted during coordination. Wednesday's advisory will say which. Until then, assuming «it is just the two from September» is exactly the kind of comfort that gets expensive.
The last five hits, in one table
Before deciding anything, look at the pattern. These are Next.js security releases since Vercel formalized the program on July 13:
| Date | Type | Versions | What happened |
|---|---|---|---|
| Jul 21 | Scheduled | 16.2.11 / 15.5.21 | First release of the program: 9 vulnerabilities (4 High, 5 Medium) |
| Late Aug | Scheduled | 16.3.3 / 15.5.24 | Critical severity, with the RCE from malicious AVIF images in image optimization among those described |
| Sep 22 | Out-of-band | 16.3.6 / 15.5.26 | Critical RCE in the ImageResponse of next/og caused by an upstream dependency: Satori |
| Sep 30 | Scheduled | 16.3.8 / 15.5.27 | Announced nine, shipped seven (1 High, 5 Medium, 1 Low); the Critical and one High postponed «due to upstream coordination» |
| Oct 14 | Out-of-band | To be published | 3 upstream vulnerabilities: 2 Critical, 1 High; two are the ones postponed in September |
Two readings of that last row. First: of the last three releases, two have been out-of-band. The monthly calendar still exists, but it is no longer the only path through which a critical vulnerability reaches production. Second: the September 30 release carries a documented trap — Next.js 16.3.7, published on September 29, is a bugfix that contains none of the security fixes, which arrived the next day in 16.3.8. «I'm on the newest version» is not the same statement as «I'm patched».
«Upstream» is the word that matters
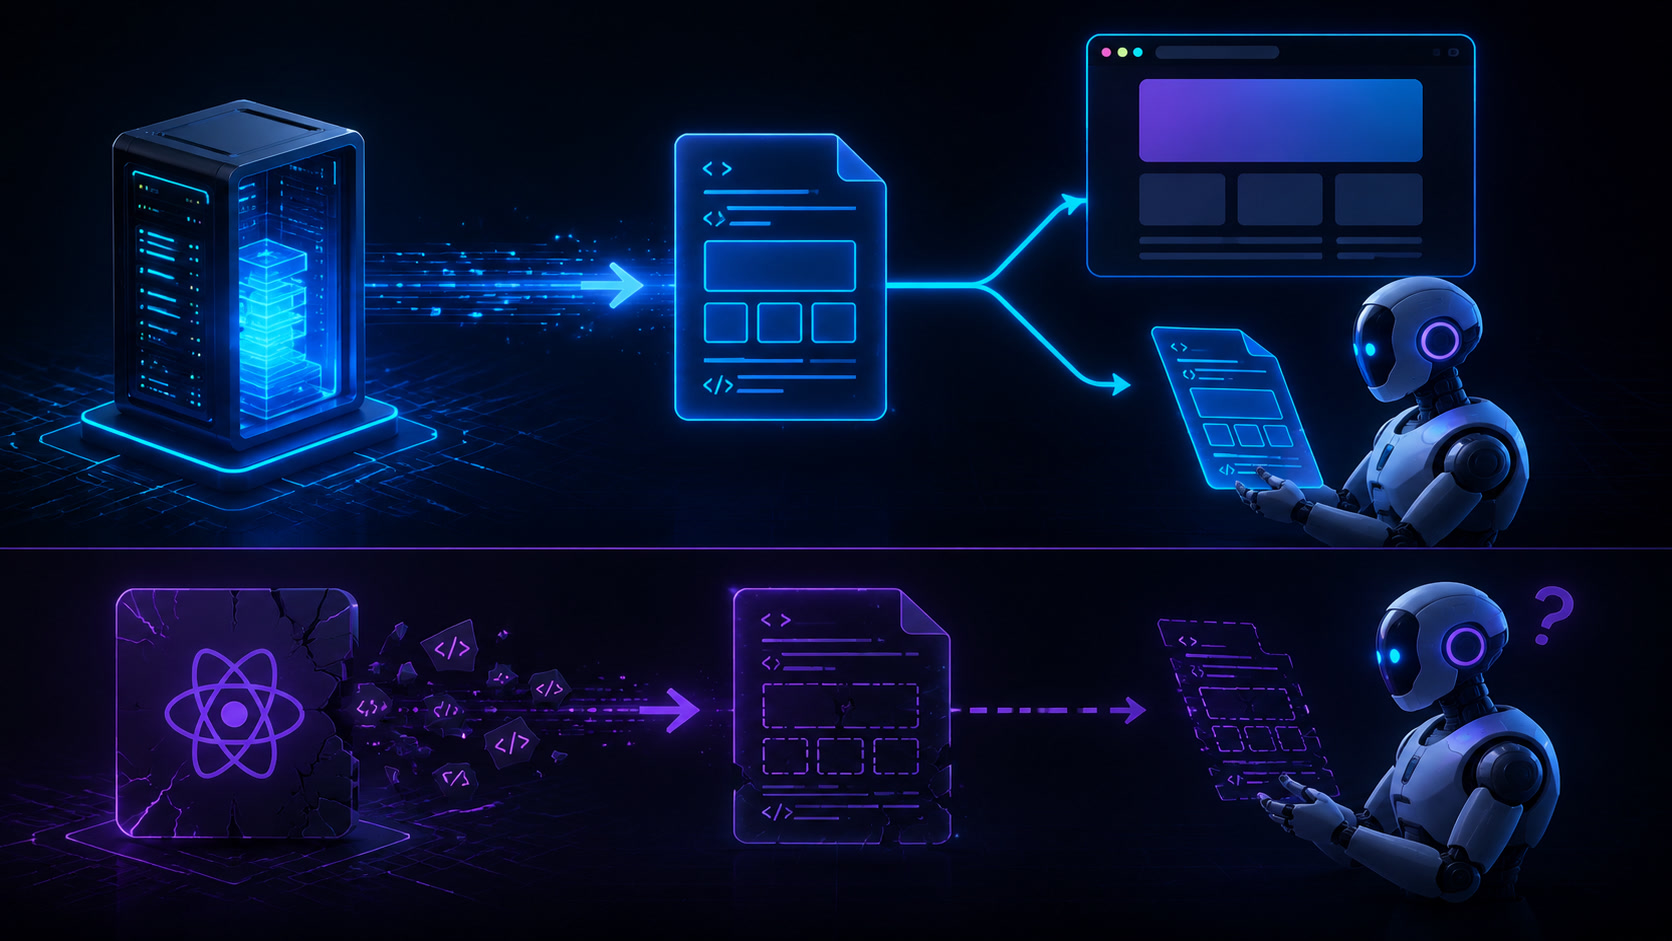
When the next/og RCE broke on September 22, the problem was not in Next.js's own code: it was in Satori, the library Next.js ships to generate Open Graph images, plus other upstream dependencies that turned a badly escaped SVG into code execution. All Next.js had to do was bump the dependency and coordinate the announcement.
That is the model repeating on October 14, and it changes how triage works. With a framework vulnerability your question is «what version am I on?». With an upstream vulnerability your question is «do I use the affected surface?»:
- Do you generate images with
next/ogorImageResponse? That is where September's RCE landed. - Do you have
images.remotePatternsconfigured? Without it, the September 30 image-optimization SSRF does not reach you; with it, it does. - Do you have rewrites proxying to your own backend? The request-smuggling family that hit Next.js in March originated in a vendored upstream library, and it only applies to that proxy pattern.
- Do you self-host ISR/SSG? The September 30 cache poisoning issues were about your server, not Vercel's.
None of those answers come out of package.json. That is why our per-project triage maps API surface before version: we wrote the same reasoning when we analyzed the Astro 7.2.4 base-path authentication patch, where the right question was whether you used basePath in middleware, not whether you were on the latest release. Our real Astro vs Next.js benchmark shows the other side of the coin: the more server runtime you carry, the more surface like this you accumulate.
What changes in the runbook when you don't control the calendar
In our Next.js patch runbook we wrote in August that the advantage of the new program was the known date: reserve a maintenance window, tell the client, prepare staging without improvising. It works when the release arrives as announced. October 14 exposes its two blind spots:
- The cadence is no longer monthly, and it does not depend on Vercel. Between July and October there were five security releases and two of them were out-of-band. If your plan assumes «the next notice arrives within a month», the October 8 notice gives you six days, not thirty.
- Announced does not mean complete. On September 30 the release content changed on the day itself: nine vulnerabilities promised, seven delivered, and 16.3.7 — published a day earlier — turned out to carry none of the fixes. The runbook can no longer take the announcement's count, or the label «latest version», at face value: verify against that day's advisory list.
This is the matrix we use on Wednesday morning:
| Project situation | What you check first | Typical decision |
|---|---|---|
| App Router with middleware, auth or Server Actions | Server surface: sessions, Server Actions, rewrites | Staging that morning, production the same day |
Self-hosted ISR/SSG or use cache | Whether you depend on server-side caching (September's advisories already applied to you) | Staging with real traffic first, production same day |
Uses next/og, ImageResponse or images.remotePatterns | The image surface where August's AVIF RCE and September's SSRF landed | High priority: ship as soon as the advisory is out |
| Exported Next.js or static site with no runtime of its own | Whether any inherited edge function or rewrite remains | Normal window, no drama |
| On 15.5.x (Maintenance LTS) | Patch within your line, no mixing migrations | Nothing like «while I'm updating, I'll jump to 16» |
That last row is not a theoretical precaution. The Cache Components decision we published on October 8 is exactly a feature improvement that deserves its own test cycle; folding it into the same commit as a critical patch is how a one-hour change becomes a sprint — and how that sprint gets postponed until someone decides it was never necessary.
What we will do on Wednesday
Our client operation does not allow «let's wait and see». Monday we close the inventory: npx next info per project, npm ls next to catch nested copies, and the list of projects touching next/og, remotePatterns, rewrites or middleware. Tuesday the upgrade branch sits ready with the lockfile diff and the smoke tests written: login, rewrite routes, OG image generation, a full build. On Wednesday, advisory in hand, we map impact → affected projects → staging → production with a rollback tag.
What we will not do: panic-ship a static site with no server surface, or postpone an auth-heavy dashboard because «we already upgraded in September». Severity comes from the advisory; urgency comes from your surface. And we already know what we will read on Wednesday, because it is what has failed twice in a row: that the fix depended on an external library and the coordination took time.
The 48 hours before, concretely
- Today: version inventory plus API-surface inventory for every Next.js project you run.
- Today: green staging — if the upgrade branch breaks, let it break before Wednesday.
- Tomorrow: rollback tag created, and a named person deciding who deploys and when.
- Wednesday: read the full advisory before touching anything — impact, affected versions, instructions — then decide with the matrix above. Next.js sums it up in one line: «Upgrade to a patched version as soon as the update is available». The discipline lives in the first part: as soon as, not whenever.
Keep one idea: the patch calendar is the best thing that has happened to Next.js vulnerability management in years, but it is no longer a guarantee. The guarantee is what you build — inventory, staging, and a decision matrix that survives a release arriving whenever an external project feels like coordinating.
Frequently Asked Questions
What is an out-of-band Next.js security update?
A patch published outside the roughly-monthly calendar Vercel formalized in July 2026. On October 8 Next.js announced an out-of-band update for Wednesday, October 14, 2026 covering three vulnerabilities in upstream dependencies (two Critical, one High). Scheduled releases arrive with a known date and an announced scope; out-of-band releases arrive when coordination with an external project allows it, which means shorter notice and content you cannot read until release day.
Which Next.js versions does the October 14 patch affect?
It is not published yet. Next.js states that the full advisories — impact, affected versions, and upgrade instructions — ship together with the update on October 14. Until then the only confirmed scope is three vulnerabilities in upstream dependencies, two of them postponed from the September 30 release. Today's patched baseline remains 16.3.8 (Active LTS) and 15.5.27 (Maintenance LTS); anything older than 16.3.6 or 15.5.26 is missing at least the recent fixes.
Should I upgrade on Wednesday, October 14 itself?
Yes, as soon as the advisory is out — Next.js says it directly: «Upgrade to a patched version as soon as the update is available». The discipline is in arriving prepared: version inventory on Monday, staging branch ready, smoke tests written, rollback tag defined. Upgrading before you have read the advisory is improvising; waiting a week is gifting an attacker the gap between a public release and your deploy.