Chrome 154 already asks before it opens your HTTP site — here's the 30-minute audit we ran on mintec.co
Chrome 154 turns on Always Use Secure Connections by default for public sites, so Chrome asks permission before loading a page that will not answer over HTTPS. What actually triggers the prompt and what does not, plus the five checks we ran against our own site on October 5, 2026.
Chrome 154 already asks before it opens your HTTP site — here's the 30-minute audit we ran on mintec.co
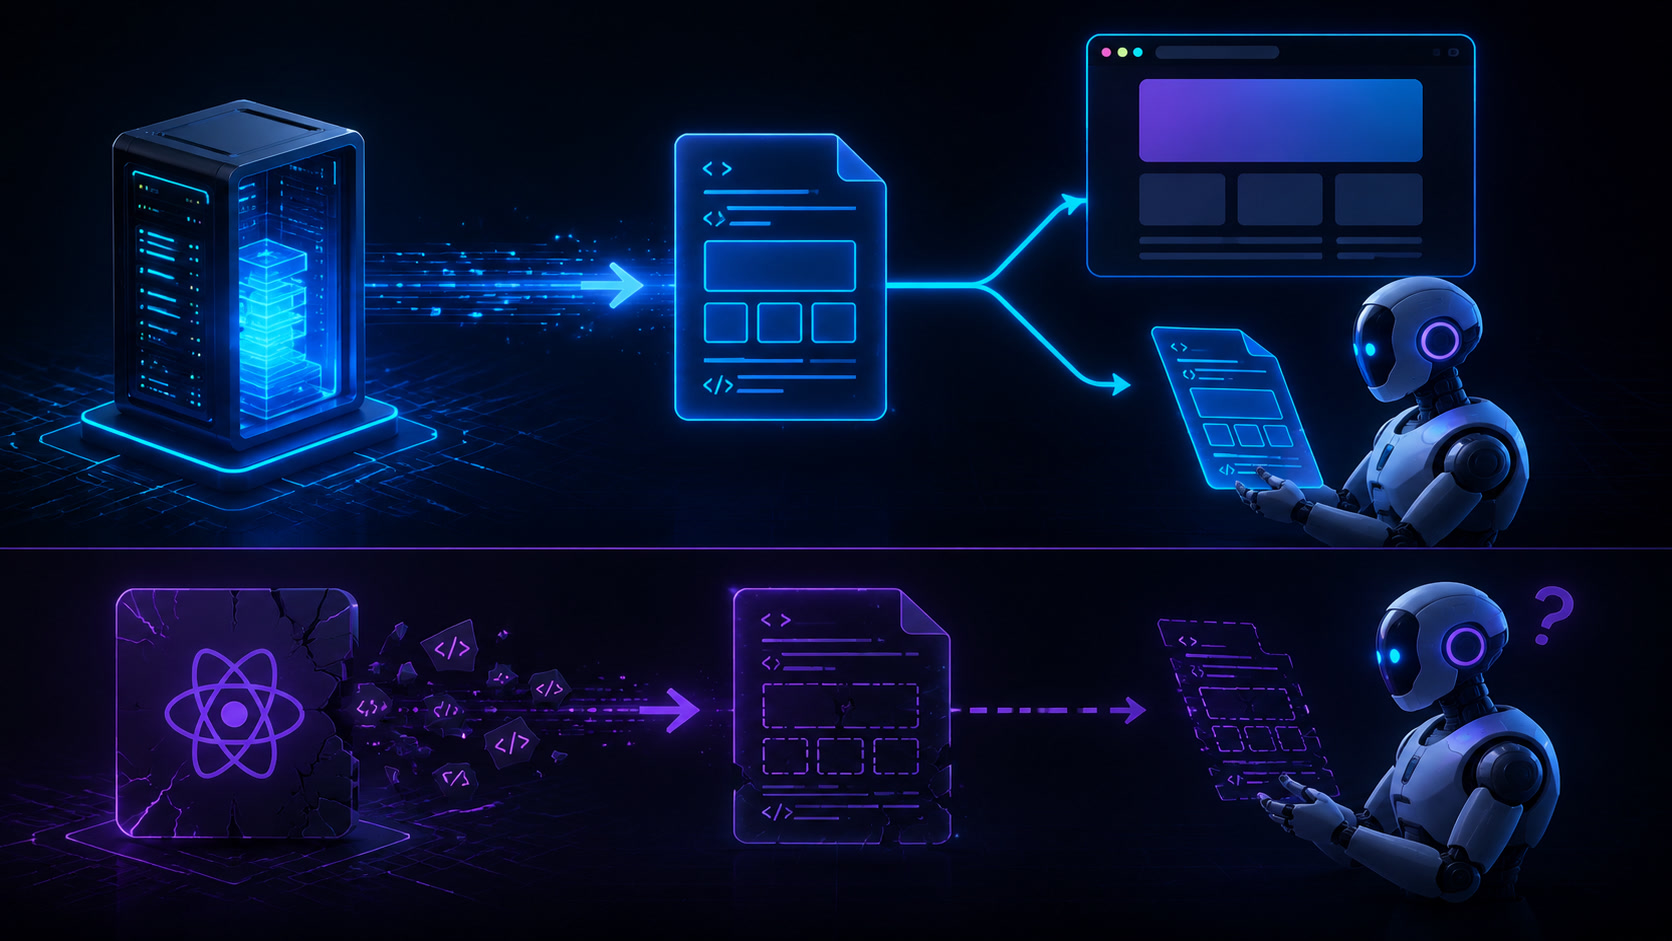
Chrome 154 has been in the stable channel since September 22, 2026, and it turns on Always Use Secure Connections by default for public sites: when someone clicks an http:// link or types one, and the site does not answer over HTTPS, Chrome asks for permission before it continues over HTTP. The part almost nobody explains is that the prompt is not a penalty on every old link. Chrome attempts HTTPS first, so most plain-text links upgrade silently and nobody sees anything. The prompt shows up only where HTTPS fails: forgotten domains, expired certificates, subdomains nobody reviews. That makes this a link-hygiene problem, not a security project.
The date you were promised is no longer the real date
Google announced it in October 2025 with a specific sentence: "with the release of Chrome 154 in October 2026, we will change the default settings of Chrome." Then, in March 2026, Chrome moved to a stable release every two weeks instead of every four, and milestones shifted without anyone updating that blog post. The result is what we verified today: the milestone Google named has been stable since September 22, confirmed by the Chrome Releases announcement for that date — the same date we published ourselves on August 26 in our two-week release cycle calendar. The current build is 154.0.8037.98, built on October 2 according to Chromium Dash.
Chromium's adoption guide, read on October 5, still says it without ambiguity: "Chrome will start asking for users' permission before navigating to HTTP pages by default in Chrome 154." So the calendar date and the milestone name no longer agree, and the practical lesson is simple: do not wait for "October" to review your site. If you want certainty about your exact build, turn the setting on and test it, which is exactly what Google recommends in that same guide.
This milestone also carries other interface changes we already covered in our Chrome 154 breakdown; what is new here is the navigation prompt, not the CSS features.
What triggers the prompt and what does not
The distinction matters because it decides in two minutes whether you have work pending. Per Chromium's adoption guide, the warning appears when Chrome could not connect over HTTPS but believes HTTP may still work:
| Situation | What the user sees | New prompt? |
|---|---|---|
http:// link to a host with valid HTTPS | Connects over HTTPS without touching HTTP | No, silent upgrade |
http:// link where HTTPS fails but HTTP answers | Full-screen permission before continuing | Yes |
https:// link and the site does not answer | Normal network error page | No, and no HTTP fallback |
| Host with HSTS and a dead certificate | Error page, no fallback | No, HSTS forbids the fallback |
| Expired or misconfigured certificate | The certificate warning as always | No, that mechanism is unchanged |
http:// resources inside an HTTPS page | Mixed content blocking as today | No, different mechanism |
| Local IPs, intranets, single-label hostnames | Exempt from the public-sites variant | No |
One operational detail that gets overlooked: Chrome remembers the user's decision for 15 days and renews it whenever the person revisits the site. You are not paying an interstitial on every visit — one per domain every two weeks. The real cost is not the bounce; it is the prompt landing on first contact: the click from a printed QR code, the link in a 2019 newsletter, the catalog PDF still in circulation.
The audit we ran on mintec.co
We sell web architecture and maintenance decisions, so our own site had to be the first client of this audit. Five checks, run on October 5, 2026:
- Root headers.
https://mintec.co/answersHTTP/2 200. It sends noStrict-Transport-Securityheader. No HSTS, no forced fallback. - Certificate. Valid from September 19 to December 19, 2026: automated 91-day rotation, no manual intervention.
- Plain-text reference census. Across
src/content/we counted 13 distinct hostnames referenced ashttp://, across 81 occurrences:
| Host | Occurrences | HTTPS answers today |
|---|---|---|
mintechn.com (legacy domain) | 45 | Does not answer |
www.mintec.co | 10 | Yes |
es.wikipedia.org | 4 | Yes |
blog.hubspot.com | 4 | Yes |
youtube.com / www.youtube.com | 4 | Yes |
www.ideasparatucomercio.es | 2 | Does not answer |
| Six other hosts (Twitter, Blogger, HubSpot, Domaintools, Postcron, Derechoaleer) | 12 | Yes |
- Real coverage. Of the 13 hostnames, 11 answer over HTTPS today — silent upgrade, zero prompts. The two that do not are exactly the ones that need a manual test with the setting enabled.
- Own domain and the
wwwsubdomain. Both answer200over HTTPS; the header finding is the same: no HSTS.
The conclusion of our own census: most of our archive is already covered by the silent upgrade, and the risk concentrates in a single legacy host with 45 references. That is the pattern we see on almost every project: the homepage is perfect and the danger lives in the old archive.
What we are changing
- Normalize the 81 plain-text references. The 45 point to a legacy domain that needs a decision about whether we still control it: if it answers over HTTPS, update the link; if it is no longer ours, unlink it. Leaving them as they are means accepting that part of the archive depends on decisions someone made in another era.
- Ramp HSTS on. Start with a short
max-age(1 day), then 30, then a year withincludeSubDomains, and only then considerpreload. Order matters: HSTS removes the HTTP fallback, so an expired certificate stops being a redirect and becomes a hard error. Do not enable it before automated renewal covers every subdomain. The site detail that forces that order is what we just saw: the root does not send the header. - Certificate inventory with an owner. The root certificate is fine; the question is the subdomains that exist only in someone's memory. An expired certificate does not trigger the new prompt — it triggers the old one — but for the user it is the same lost conversion.
- A fixed monthly check. Two commands in the maintenance routine: HSTS header present and certificate days remaining. For the reasoning behind our hosting decision, see Cloudflare Pages to Workers with Astro.
The 30-minute audit
- Turn the new behavior on at
chrome://settings/security→ Always Use Secure Connections → Warn on insecure public sites. That way you test the future yourself instead of trusting a blog date. - Walk your twenty real entry points: campaign landing pages, archived newsletters, printed QR codes, PDFs, documentation, support links. That is where the domains normal traffic never touches will show up.
- Census your repository:
grep -rhoE 'http://[a-zA-Z0-9.-]+' src/ | sort | uniq -c. It returned 13 hostnames and 81 occurrences for us; in repos with more history the number climbs fast. - Check each hostname over HTTPS:
curl -sI https://yourdomain/. If it answers, silent upgrade and you are done. If it does not, that is your pending work. - Read your header:
curl -sI https://yourdomain/ | grep -i strict-transport. If nothing comes back, the fallback is still open. - Confirm the
http→httpsjump at the edge and that certificate renewal covers every subdomain with its own traffic.
Chrome 154's prompt does not change how the web is built: it changes what it costs to leave rubble lying around. Your homepage is ready; the work is in the links nobody has looked at in years, and a half-hour audit puts them in front of you before a user ever sees the permission screen.
If you would rather have someone run this review against your site before touching anything, we do it as part of web design and development maintenance, not as a separate project.
Frequently Asked Questions
Does Chrome 154 warn on every http:// link?
No. Chrome tries HTTPS first. The full-screen prompt only appears when a site will not answer over HTTPS but the browser believes HTTP may still work. If the host has a valid certificate, the old link upgrades silently and the user sees nothing.
How do I test my site against the new behavior?
Open chrome://settings/security, turn on Always Use Secure Connections and pick Warn on insecure public sites. Then walk your twenty real entry points: campaign landing pages, old newsletters, printed QR codes, PDFs and documentation links.
Does HSTS prevent the prompt?
Yes. If the site sends a Strict-Transport-Security header, Chrome never falls back to HTTP, so there is no prompt. The flip side counts too: once the fallback is gone, an expired certificate becomes a hard error, which is why HSTS goes on only after certificate renewal is proven across every subdomain.
Does this affect Google rankings?
It is not a ranking signal. It is friction at first contact: a full-screen permission in front of a landing page that cannot answer over HTTPS, with the conversion cost that implies.